What Conditional Access actually does
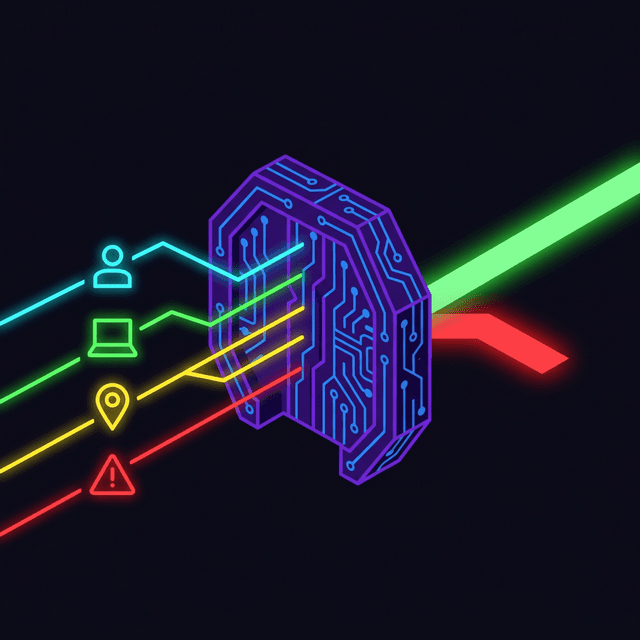
- Who is authenticating (user, group, service principal)
- What they're trying to access (specific app, all apps, admin portals)
- What device they're on (managed/unmanaged, compliant/non-compliant, platform)
- Where they're coming from (location, named network, country)
- What risk signals are active (Entra ID Protection scores for sign-in risk and user risk)
The baseline everyone should have
What I've seen go wrong
Device compliance as a gate
- Build compliance policies
- Deploy to managed devices, verify they pass
- Enable Conditional Access requirement in report-only
- Review the report-only logs for unexpected blocks
- Switch to enforce
Monitoring
- Failures due to non-compliant devices (often legitimate issues to fix)
- Blocks from unfamiliar locations (often noise, occasionally real)
- Blocks due to user risk (worth investigating each one)
Next post: endpoint hardening as a Zero Trust control — because Conditional Access requiring a "compliant device" is only as good as what your compliance policies actually check.